Your ISMS is ready for the Stage 1 certification audit
Create relevant treatment plans and map controls for a successful Information Security Management System (ISMS)
A step-by-step guide to ISO 27001 certification: objectives and scope, assets, risks, controls, documentation and the Stage 1 and 2 audits.
Create relevant treatment plans and map controls for a successful Information Security Management System (ISMS)
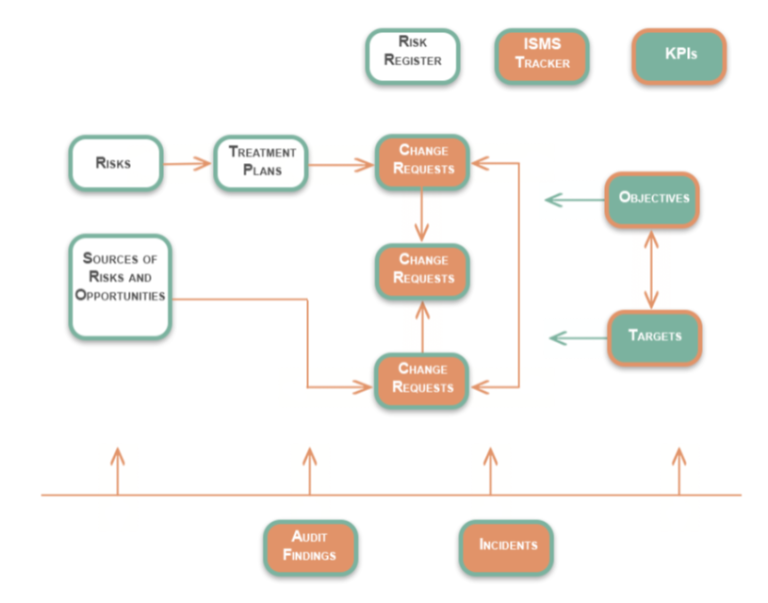
Find out how to create an efficient ISMS tracker to track your items and relevant evidence for ISO 27001
Learn how to write successful ISO 27001 documentation to ensure certification.
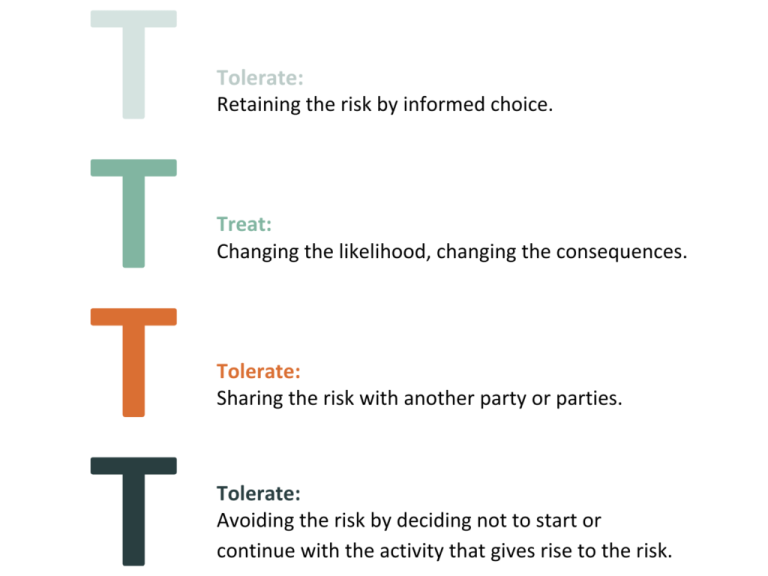
Create relevant treatment plans and map controls for a successful Information Security Management System (ISMS)
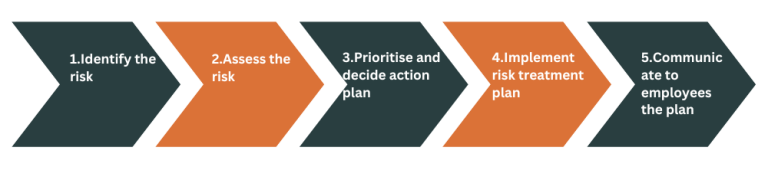
Learn how to adopt a risk-based mindset and identify your risks for your ISO 27001 risk management documentation
Learn how to define your ISO 27001 information assets and build an asset register for successful certification.
Start your journey toward ISO 27001 accreditation by setting clear, concise strategic objectives.