ISO 27001
[Headline: the outcome of ISO 27001, the risk it reduces]
[One line on who it is for and what changes once it is in place]
[Photo: real, ISO 27001 work]
Organisations we’ve worked with
[Partner logo]
[Home Office]
[Partner logo]
[End customer logo]
[Partner logo]
[End customer logo]
[Partner logo]
[End customer logo]
[End customer logo]
[Partner logo]
[End customer logo]
[Partner logo]
[End customer logo]
[Partner logo]
[End customer logo]
[Partner logo]
In plain terms
What is ISO 27001?
[Two or three sentences defining ISO 27001 and the management system behind it.]
Outcomes
What changes once it is in place
[Outcome 1]
[One line]
[Outcome 2]
[One line]
[Outcome 3]
[One line]
How we help
End-to-end support for ISO 27001
Consultancy and implementation
[What this service means for ISO 27001]
Auditing
[What this service means for ISO 27001]
Training
[What this service means for ISO 27001]
Knowledge and information management
[What this service means for ISO 27001]
Process improvement
[What this service means for ISO 27001]
Our proven process
Ready for the Stage 1 audit in five weeks
Each step has its own guide. Read the ISO 27001 guide.
Starting your journey
Build a foundation of knowledge around ISO 27001, determine your scope and strategic objectives.
Defining your information assets
Define your assets and build an ISO 27001 asset register.
Identifying your risks
Adopt a risk-based mindset and identify, assess, accept or treat your risks in an ISO 27001 risk register.
Treatment plans and controls
Create risk treatment plans, options, controls, and a statement of applicability.
Writing documentation
Understand how to write correct ISO 27001 documentation, from what the standard demands to how to store and update it.
Build an ISMS tracker
Create and operate an ISMS tracker: what to track, the evidence needed, and how the tracker should run.
Operating your ISMS and undergoing audits
Operate your ISMS and go through the Stage 1 and Stage 2 audits to achieve certification.
Case studies
See how others did it
The detail
ISO 27001 in depth
Overview
Everything you need to get ready for the Stage 1 audit in just 5 weeks.
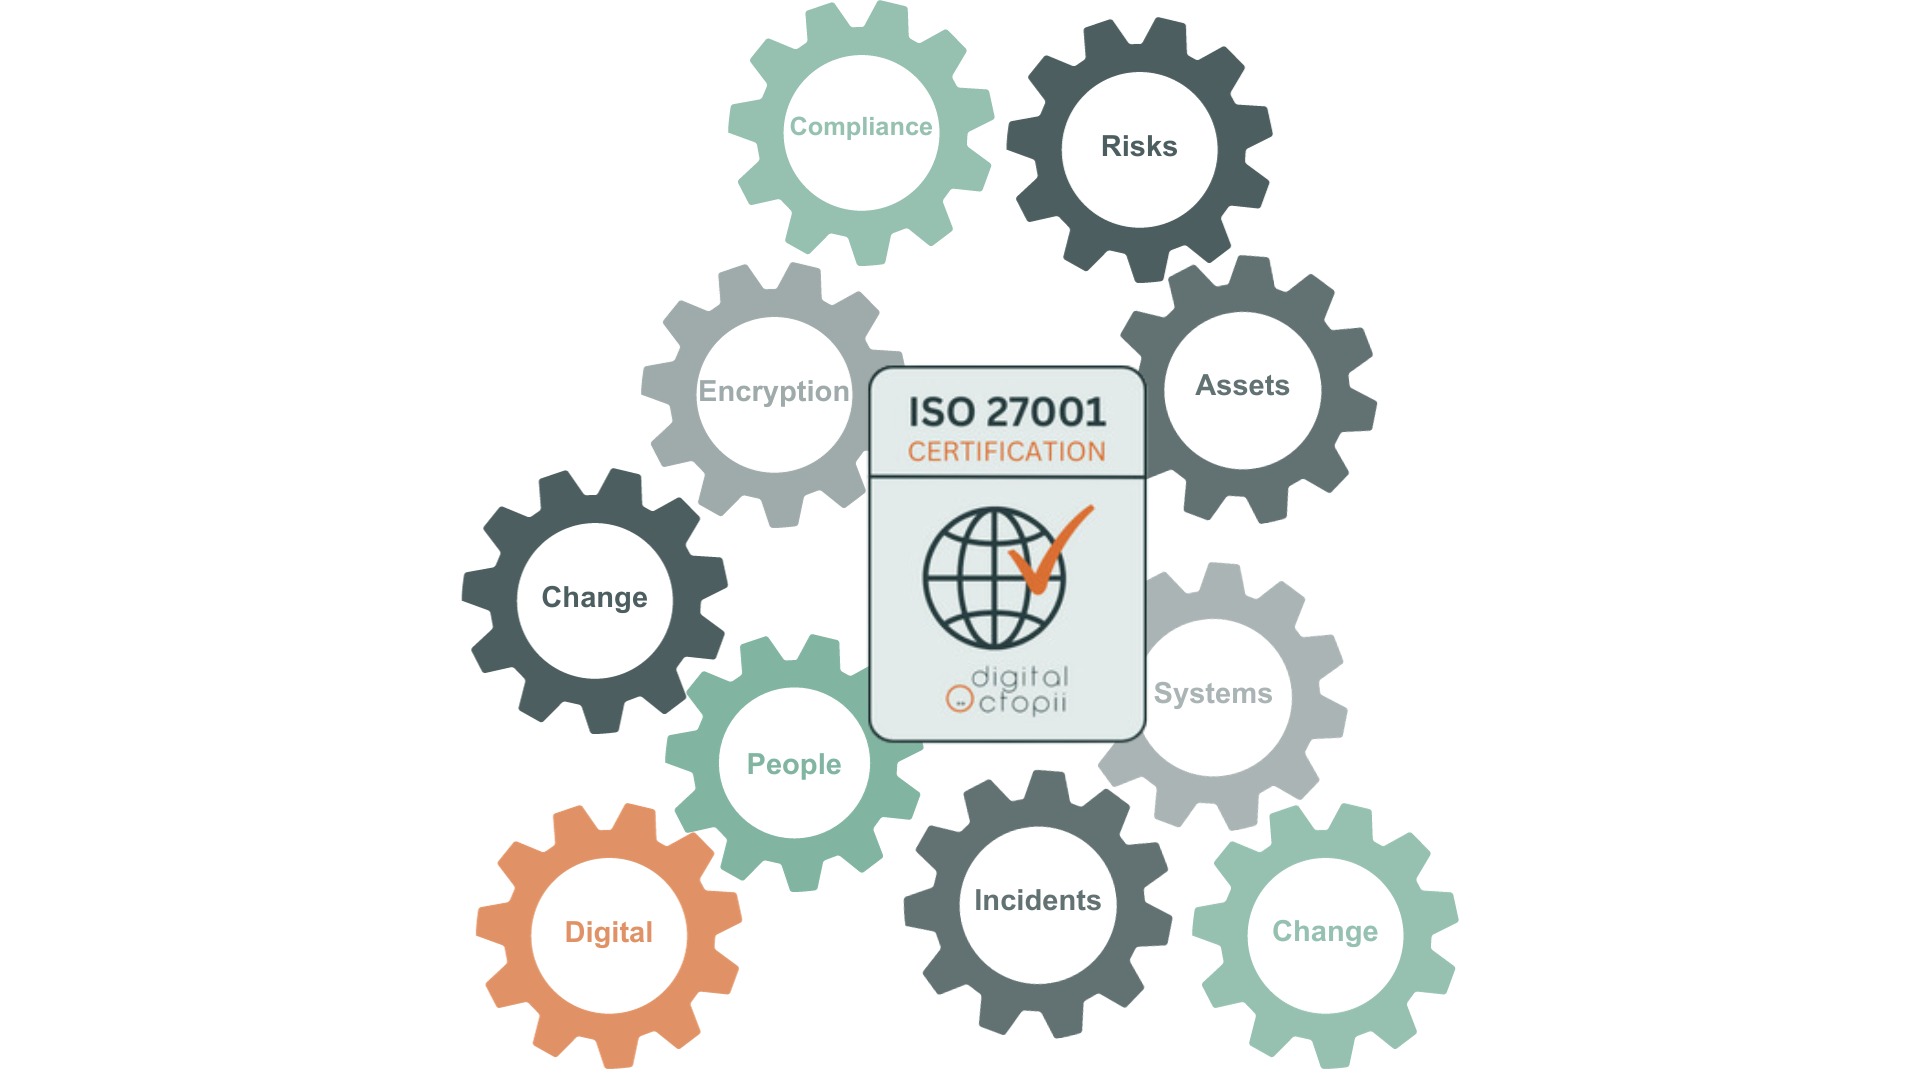
What is ISO 27001?
What is ISO 27001 and how it can help your organisation.
In this article, you’ll learn about the BS EN ISO/IEC 27001 Information Security standard. You will learn what the standard is, its purpose, benefits and why it could make a difference to your organisation
Do you need to certify to ISO 27001 at the request of a client but you’re not sure where to start?
Between our self-help blog posts and consultancy services, we’ve got you covered. Find out if you’re ready for certification with our compliance checklist.
What makes our consultancy programmes different?
Most certification programmes offered by ISO consultants are tailored to organisations with very large IT departments, comprised of several distinct teams. If your IT team is structured differently that means you waste your time and resources on drafting documentation that is not relevant to your business; and building an ISMS that’s more complicated than it needs to be.
Only do the necessary work to certify your business quickly and cost-effectively.
Our proven process can get your business ready for the Stage 1 audit in just 5 weeks
Read our journey to ISO 27001 certification article to find out more
Need a safe pair of hands?
The penny dropped for us on the very first call with Digital Octopii where our ISO 27001 consultant explained the entire process and objectives, providing us with a good understanding of what we were trying to achieve by certifying.
Simon FrancCEO of Kulpa
We had an ambitious target to obtain 4 accreditation in under 12 months, there was no way we could have accomplished this without your guidance and support. You have been great to work with and made this an enjoyable process for the whole team. Through your guidance we have become more structured, efficient and compliant, opening up many more opportunities for the future. Thank you for the very professional service you have provided.
Barry HigginsDirector at OSS
We passed stage 2! Many thanks for all your support and advice – it’s been absolutely invaluable. We’d never have passed without it!
Mark WightmanCTO at Aluma.io
Ask Elisabeth about achieving ISO 27001 certification
Send
Related standards
Works well alongside
Free downloads
Templates and guides
ISO 27001 risk register template
Free download
ISO 27001 asset register template
Free download
Example ISO 27001 scope statements
Free download
Common questions
How long does ISO 27001 certification take?
[Answer]
How long does certification last?
[Answer]
Who needs ISO 27001?
[Answer]
What is the difference between ISO 27001 and Cyber Essentials?
[Answer]
Where do we start?
[Answer]
Next step
Speak to an expert
Tell us which standard your client has asked for, and we’ll tell you what it takes.
- [What happens next, point 1]
- [What happens next, point 2]
- [What happens next, point 3]
Or call 01780 769799